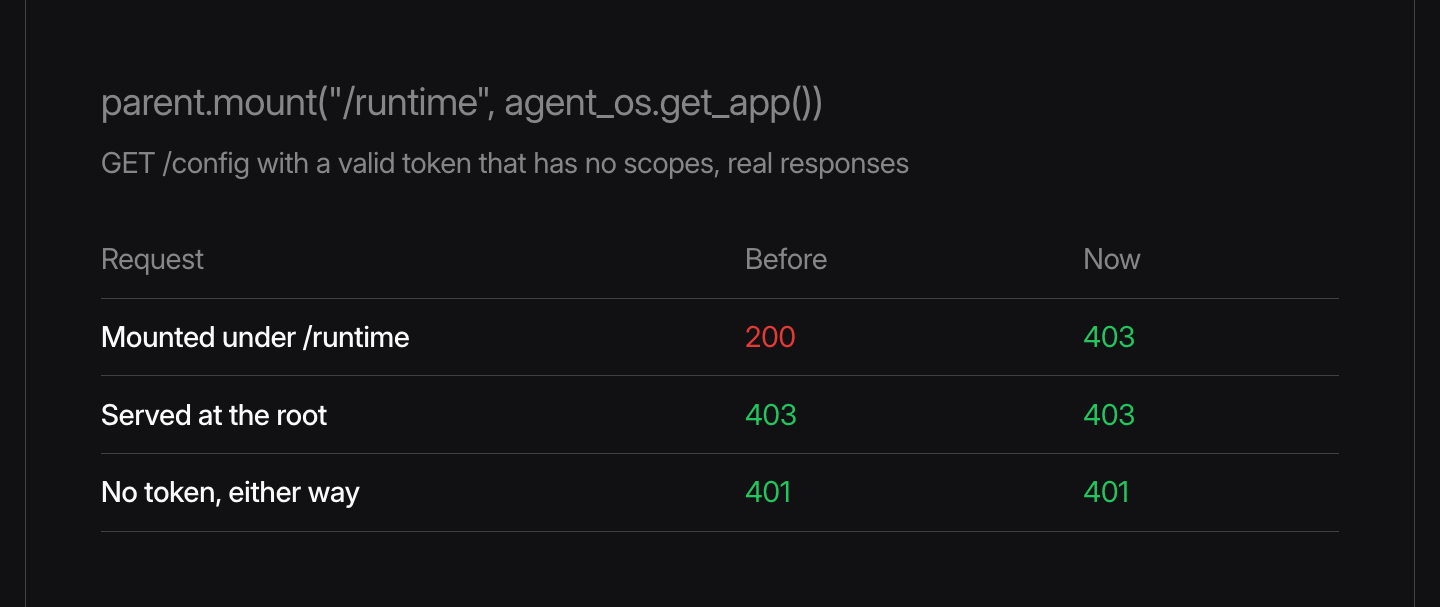
Agno's AgentOS now checks token scopes against the route inside AgentOS, whatever the mount prefix, with or without a PublicSurface. The permission check used to look up each route's required scopes with the full request path, prefix included. Under a mount like /runtime, the check found no requirement. A valid JWT or service-account token with no scopes could then read management routes such as /config, /sessions, /metrics and /schedules.
parent = FastAPI()
parent.mount("/runtime", agent_os.get_app())
AgentOS always rejected requests without a valid token, and the bug never affected AgentOS apps served at the root.
If you mount AgentOS inside another application and use JWT or service-account authorization, upgrade.
Learn more about authorization and mounting AgentOS on an existing app in the documentation.
Frequently asked questions
Yes. Whatever the mount prefix, and with or without a PublicSurface, AgentOS matches scopes to the route inside AgentOS.
The bug affected AgentOS apps mounted under a path prefix, such as /runtime, that use JWT or service-account authorization. The bug never affected AgentOS apps served at the root, and AgentOS always rejected requests without a valid token.
Upgrade Agno if your AgentOS runs mounted inside another application with JWT or service-account authorization. Read more about authorization.