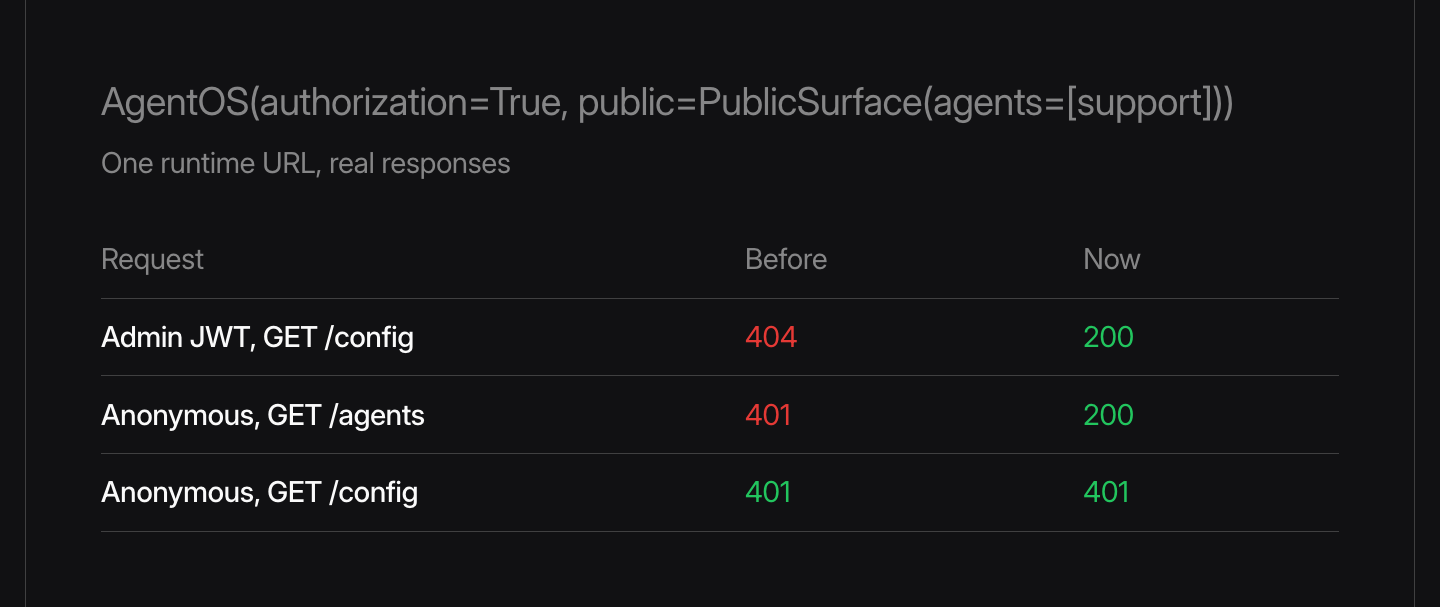
You can now set authorization=True on an AgentOS that uses PublicSurface, and manage that AgentOS from the Control Plane. The combination used to break in both directions. A valid admin token got a 404 from /config and the component routes, and AgentOS rejected anonymous chat.
from agno.os import AgentOS, MCPConfig
from agno.os.public import PublicSurface

agent_os = AgentOS(
    id="public-support",
    db=db,
    agents=[support],
    authorization=True,
    public=PublicSurface(agents=[support], mcp=True),
    mcp=MCPConfig(tools=[service_description], default_tools=False, stateless=True),
)
Set JWT_VERIFICATION_KEY to the Control Plane's public key so AgentOS can verify its tokens.
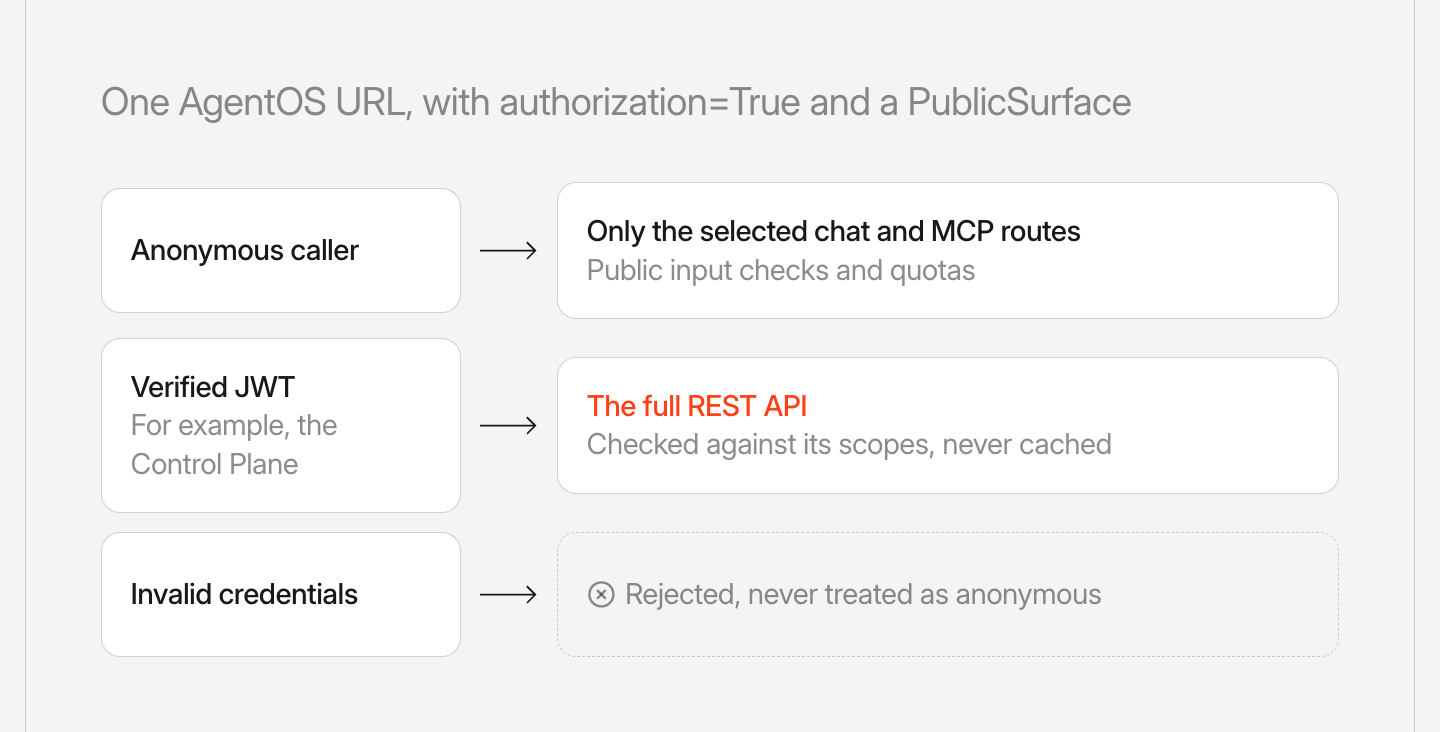
On one runtime URL, AgentOS now handles each caller by its credentials.
- Anonymous callers reach only the chat and MCP routes you selected, with the same input checks and quotas as before.
- Verified JWTs reach the full REST API, subject to their scopes. AgentOS marks those responses private and never caches them.
- AgentOS rejects invalid credentials. A bad token never falls back to anonymous access.
Public workflow WebSockets on this AgentOS now reach their authentication handler. AgentOS applies a shared connection quota, a cap on pending connections per worker, a fixed authentication deadline and a limit on failed attempts.
If you already combine authorization=True with PublicSurface, AgentOS now accepts anonymous requests to your selected public routes. Public MCP keeps its explicit tool list and quotas even for admin tokens. Use mcp_auth if MCP itself should require sign-in. Without authorization=True, a public deployment still closes its management routes.
See the cookbook, and learn more about Public Surface and the Control Plane in the documentation.
Frequently asked questions
Yes. Set authorization=True on an AgentOS that uses PublicSurface. Anonymous callers reach only the public routes you selected, and verified JWTs such as the Control Plane's reach the full REST API.
An AgentOS that combined authorization=True with PublicSurface returned 404 from /config and the component routes, even for a valid admin token. AgentOS now serves the full REST API to verified JWTs, subject to their scopes.
Even for admin tokens, public MCP keeps its explicit tool list and quotas. Use mcp_auth if the AgentOS MCP server itself should require sign-in.